InCommon Certificate Enrollment Guide
Learn how to request an InCommon Digital Certificate.
**Action Required: InCommon/Certinext eMsign Certificates
InCommon/Certinext eMsign Certificates Must Be Re-Issued Before November 16, 2026.Google Chrome and Mozilla Firefox are distrusting eMudhra/eMsign root certificates effective November 16, 2026. To prevent service disruptions, all active eMsign certificates must be re-issued under the company's new replacement Certificate Authority (CA), SSL.com. See information below.
InCommon/Certinext eMsign Certificates Re-Issue
What Is Happening?
- Distrust Deadline: Google and Mozilla will officially stop trusting newly issued certificates from the eMsign G1 root on the evening of November 16, 2026.
- The Replacement: InCommon has announced that SSL.com will replace eMsign/eMudhra.
- Trust Verification: The SSL.com trust chain is fully compliant and accepted by all major platforms, including Apple, Microsoft, Google, Mozilla, and Oracle.
What You Need to Do – will update here when the new CA is enabled.
- Monitor the Portal: Await the activation of the new SSL.com CA within the InCommon/Certinext GUI.
- Re-issue Certificates: Once enabled, log into the portal and immediately re-issue your existing eMudhra/eMsign certificates using the SSL.com CA.
Note from Certinext:
"We're providing advance notice of our upcoming production release supporting the SSL.com Certificate Authority (CA) connector, currently targeted for November 7–8, with a strong possibility of an earlier deployment date. Final release preparations and required approvals are still underway, and we'll confirm the exact timing once these are complete.
Important note on availability: We're looking forward to enabling SSL.com certificate issuance across InCommon member accounts. Please note that production deployment does not mean immediate availability to the community, as final production testing and validation must be completed before broader enablement. The initial rollout will support Domain Validated (DV) certificate issuance, and we'll announce availability separately once confirmed.
Our team remains committed to making this functionality available as quickly as possible while ensuring a reliable experience for our members."
CERTInext
UC San Diego is using the CERTInext platform a US-based certificate lifecycle management (CLM) and Public Key Infrastructure (PKI) platform, as our InCommon Service certificate authority.
Registration and login
Register
To register for access, email pki-certs@ucsd.edu with your name, UC San Diego email, and your work group. Allow 24 hours for a response.
Follow the activation link in the onboarding email. Create a local account on the CERTInext console. This allows CERTInext to authenticate your access, and provide an alternate login if UC San Diego's SSO interface is down.
Login using SSO
Go to the CERTInext Institutional login page and choose the orange "Sign in with your institution" button. Follow the prompts to sign in with UC San Diego's Single Sign On (SSO) option.
Once you have logged in, you will see the user dashboard.
Choose your group. If your group is not in the list, select UCSD.

Note: If you have issues, email pki-certs@ucsd.edu. Include any error messages.
Create a new certificate
Step 1 - Choose Product & Validity
Click the black New Certificate button in the upper-left menu bar to create an enrollment request. Then follow the 7-step certification process.

In the Certificate menu, start with Step 1, Product and Validity Group.
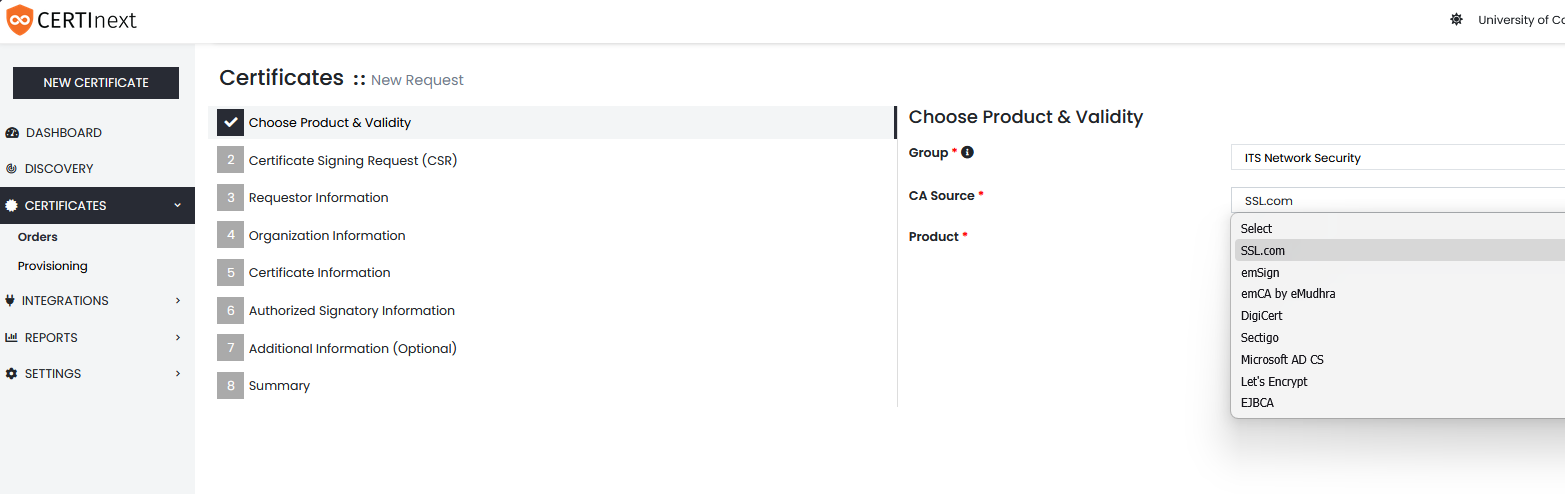
- Complete the enrollment screens and be sure to include your contact information so you can receive the download links by email.
- Group: If your group or department is not listed, select UCSD as the default. To request that your group be added to the platform, email pki-certs@ucsd.edu.
- CA Source: Use the dropdown to select SSL.com as the CA. Do not select any other.
- Certificate Type: SSL/TLS Certificates
- Product:
- InCommon OV SSL certificate: Choose this if your webserver responds to one domain name.
- InCommon OV SSL UCC certificate: For multi-domain version of the above. For example, if your webserver responds to more than one name.
- If you select the UCC certificate type, you can use the drop down to select the number of SANs up to 100. Above that number is not recommended by our provider to avoid DNS and validation strain.
- When complete, on the bottom right corner, choose the black Next button.

Step 2 - Certificate Signing Request

Step 3 - Organizational Information
You may need to add UC San Diego's organization information:
Organization: University of California, San Diego
Address: 9500 Gilman Drive
City/State/Zip: La Jolla, CA 92093

Step 4 - Organization Representative Information
The organizational Representative will be pre-filled. Fill in your contact information under Certificate Download Delegation. Your email ID is your UC San Diego email address.

Step 5 - Certificate Information
Check the content to make sure it is correct. The domain names should autopopulate from the certificate you previously added.

Step 6 - Additional Information

Step 7 - Summary and Payment

Options
Managing Certificates
- Any enrollment requests you submit will remain in your queue for easy management.
- The dashboard displays important information such as upcoming expirations and certificate status.
- You can renew or revoke certificates from the **Orders** queue (accessible from the left-hand menu).
Revoke Certificate
To revoke a certificate, at the top right of the screen choose the three dot "hamburger menu" option. The option to track, revoke, and download a certificate will appear.
